DPDP Compliance Services
DPDP compliance built aroundconsent, audit, and real grievance handling.
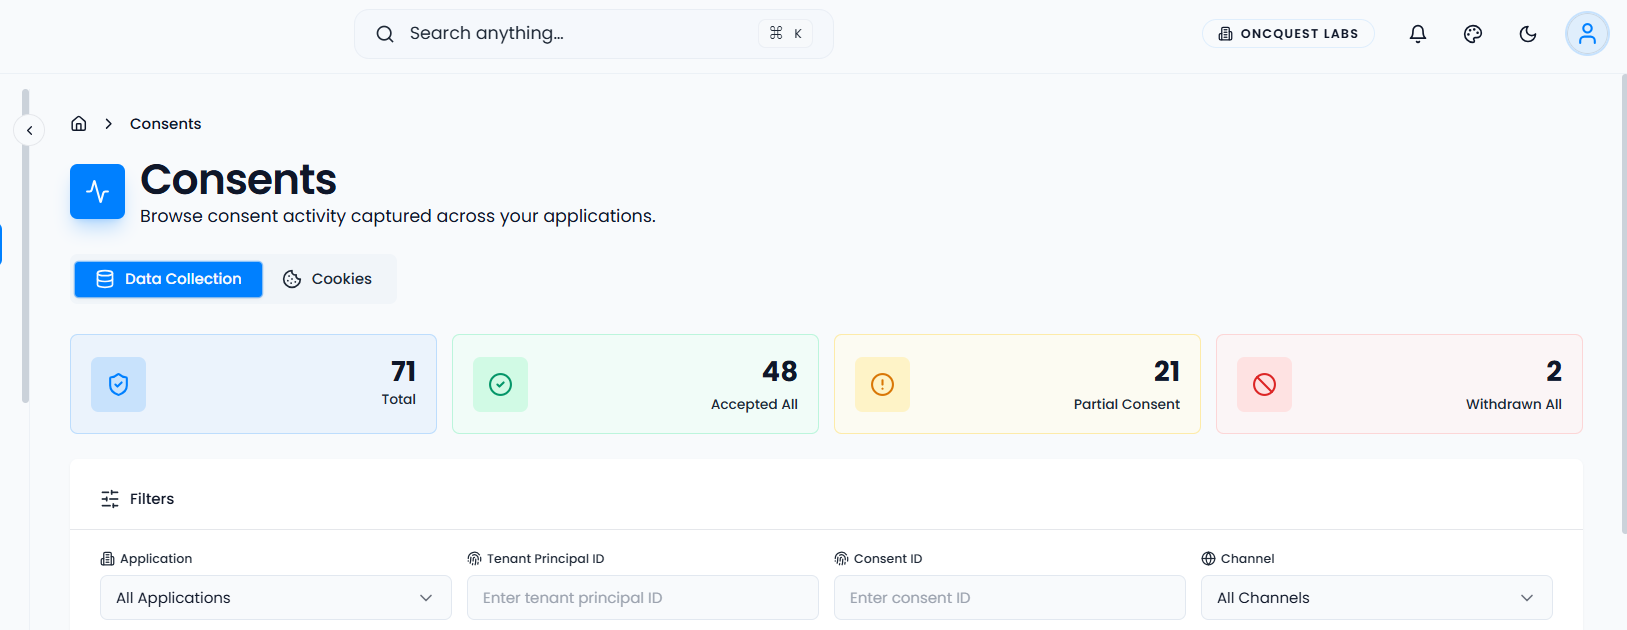
- Consent & cookie management with Indian-language notices
- Compliance gap assessment against your current data practices
- Logged grievance redressal, not email threads that disappear
- DPO and legal advisory through our certified partner network
What the Act actually requires
Service pillars covering the DPDP compliance lifecycle
Maximum penalty for inadequate security safeguards
Regulatory breach follow-up notification window
Deadline for full operational compliance
Customers trusting Digital Anumati across India
8 pillars · 3 phases
Key pillars of our DPDP compliance practice
Each pillar maps to a specific obligation under the DPDP Act, 2023 — built and delivered directly, or through our certified partner network where noted.
- 01
Consultation & Gap Assessment
Understand your compliance status
- Sec 802
Re-Audit & Compliance Review
Verify controls stay compliant
- Sec 5, 603
Consent & Cookie Management
With Indian-language support
- Sec 4, 604
Notice & Consent Framework
Purpose-based, multilingual
- Sec 1305
Grievance Redressal Workflow
Logged complaint handling
- Sec 3306
Audit-Ready Records
Consent & compliance documentation
- Sec 1007
DPO Advisory
Structured oversight, via our partner network
- Sec 8, 1308
Legal & Advisory Support
Through our CA & law-firm partners
Services & platform
DPDP compliance services & consent platform
What each pillar looks like in practice.
Consultation & Gap Assessment
Understand where your current data practices stand against DPDP obligations before you spend on fixing the wrong thing.
- Review of current data collection and processing workflows
- Assessment of existing consent mechanisms and verifiability
- Data retention and deletion practice review
- Prioritised remediation roadmap, not just a findings list
- Data inventory
- Consent verifiability
- Retention & deletion
- Remediation roadmap
Digital Anumati vs. traditional approaches
Most teams stitch together a cookie-banner plugin, a compliance consultant, and a spreadsheet. Here's the difference.
Consent & cookie management platform
Point Consent ToolsYesConsultantsNoDigital AnumatiYesNotices in Indian languages
Point Consent ToolsRareConsultantsNoDigital AnumatiYesGap assessment & remediation plan
Point Consent ToolsNoConsultantsYesDigital AnumatiYesGrievance workflow, logged and tracked
Point Consent ToolsNoConsultantsNoDigital AnumatiYesDPO & legal advisory access
Point Consent ToolsNoConsultantsYesDigital AnumatiVia partner networkAudit-ready records, exportable
Point Consent ToolsPartialConsultantsNoDigital AnumatiYesOngoing platform, not a one-time report
Point Consent ToolsYesConsultantsNoDigital AnumatiYesSingle vendor to manage
Point Consent ToolsNoConsultantsNoDigital AnumatiYes
Expert managed services for DPDP compliance
Extend your compliance program with services that go beyond the platform.
DPO Advisory
Governance oversight and grievance-handling guidance through our certified DPO partner network.
Legal & Compliance Advisory
Notice drafting, consent framework review, and Data Processing Agreement guidance through our CA and law-firm partners.
Grievance & Rights Support
Help setting up and operating the Data Principal request and grievance process end to end.
Let's map out your compliance path
May 2027 is closer than it looks — start with a roadmap built for how your organisation actually collects and uses data.
Book a ConsultationWhat you get when you work with us
Unified Consent & Cookie Suite
Consent capture, cookie compliance, and preference management in one platform, not three vendors.
Data Principal Grievance Portal
A logged process for access, correction, erasure and grievance requests — with SLA tracking.
Automated Consent Audit Trail
Every consent event, notice version, and withdrawal kept in a single exportable record.
Partner-Backed Advisory Access
DPO and legal advisory support through a vetted network, without hiring an in-house team.
What this looks like by sector
The Act applies to everyone, but what “reasonable safeguards” look like changes by sector.
BFSI & NBFC
Customer KYC and transaction data handled under both DPDP and existing RBI expectations.
Healthcare
Patient records and appointment data treated as sensitive by default, with tighter access logging.
D2C & E-commerce
High-volume checkout and marketing consent across web and app.
IT & SaaS
Customer and employee data processed on behalf of other Data Fiduciaries.
Education
Student and guardian data, with the Act's added verifiable-consent requirement for minors.
Book your DPDP compliance consultation
Get a technical and process assessment of your organisation's current data practices.
- Current data collection and processing workflows
- Consent mechanisms and how verifiable they are
- Retention, deletion and grievance handling practices
Fields marked * are required.
Book a Consultation
Tell us how your organisation collects and uses data. We'll reach out within one business day.